Let's meet!
I'm Wiem Abbassi,
AI &
Cybersecurity Engineer
Building intelligent systems that are secure, scalable, and human-centric
LLMs • RAG • Threat Intelligence • SOC Pipelines • ML • Python
Let's meet!
Building intelligent systems that are secure, scalable, and human-centric
LLMs • RAG • Threat Intelligence • SOC Pipelines • ML • Python
A selection of projects spanning AI, cybersecurity, and full-stack development.
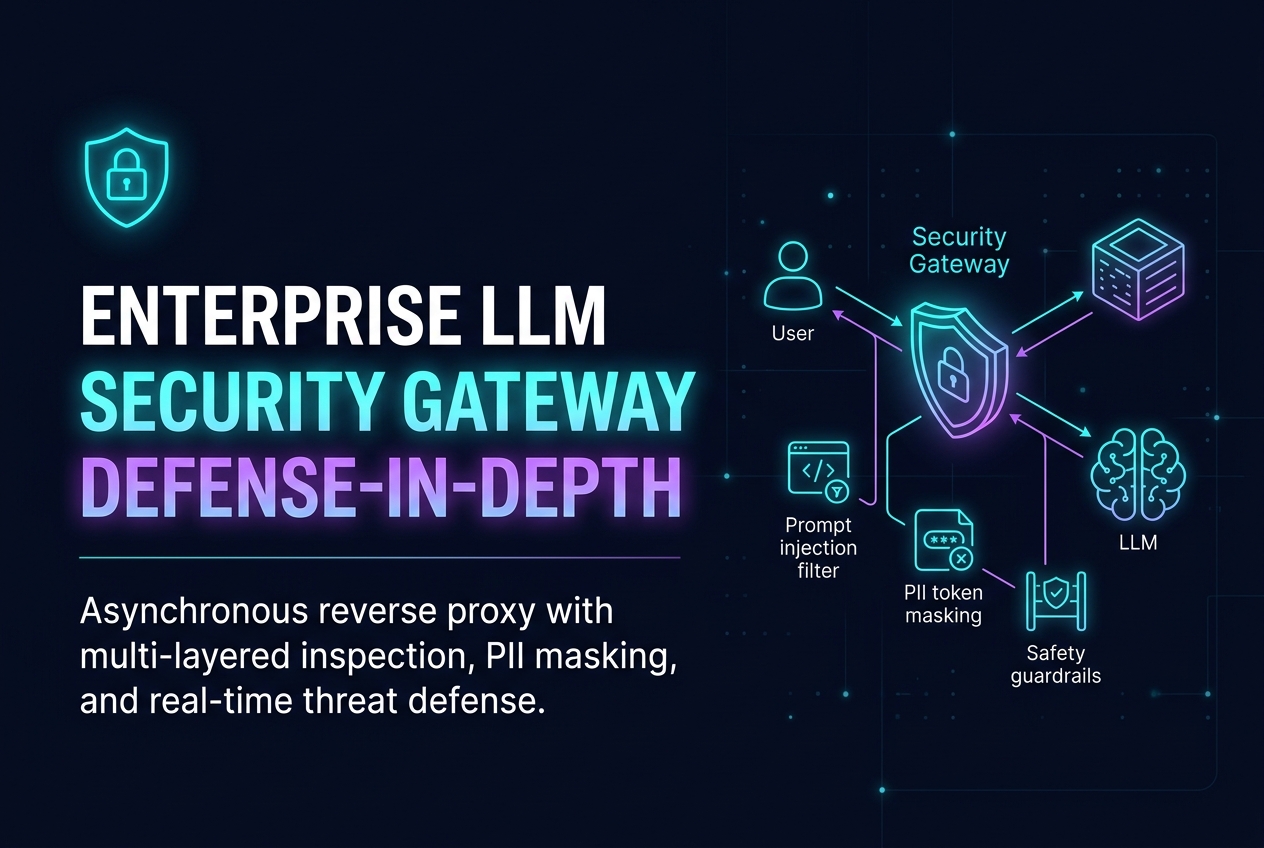
Asynchronous multi-layered reverse proxy securing enterprise LLMs against prompt injection, jailbreaks, and PII leaks.

1st place Automated threat intel pipeline with human-in-the-loop adaptability.

Translate natural language into validated Splunk, KQL, and Elasticsearch queries using local LLMs.

Voice-based Q&A in Tunisian Arabic for olive growers with disease classification and RAG safeguards.

Hands-on red teaming of LLMs with Mistral 7B, prompt injection, and OWASP-guided mitigation strategies.
▼ Click for detailsI'm Wiem Abbassi, a Computer Science graduate from Higher Institute of Computer Science with a deep passion for AI, cybersecurity, and building systems that make a real impact. My work spans LLM-powered security tools, machine learning, and full-stack development.
I specialize in building AI-powered security solutions from threat intel pipelines and LLM-based detection systems to RAG applications and multi-agent architectures. Every project is driven by a commitment to real-world impact and continuous learning.
Computer Science graduate with hands-on experience in AI engineering, cybersecurity, and business intelligence.
currently at Higher Institute of Computer Science
Degree by Higher Institute of Computer Science
in the RFC agency
in the RFC agency
in the MAVISION agency
at Securinets ISI
at Freeways ISI
Competitive programming achievements and academic distinctions.


Professional certifications from industry leaders in AI, cloud, and data science.
Deep dives into AI security, LLMs, and cybersecurity — published on Medium.

A hands-on breakdown of every OWASP risk for LLM applications — from prompt injection and training data poisoning to insecure output handling — with real-world attack scenarios and mitigation strategies.

A deep technical walkthrough of building a 15-subsystem defense-in-depth security gateway — covering DeBERTa-v3 prompt injection detection, PII masking with Presidio, Llama Guard evaluation, and LoRA retraining workflows.
Exploring production-grade LLM observability — from OpenTelemetry distributed tracing and behavioral anomaly detection to autonomous retraining pipelines that keep models secure and reliable at scale.
Have a project, question, or just want to say hi? Send me a message!
+216 20 09 60 70


